A public intake
An intake page and a security.txt file, so a report has a front door that is not one person's email.
CRA evidence
A clear path from "someone reported a bug" to a recorded decision, a fix and an advisory, for the whole support period.
Checked against the regulation on 16 Oct 2026 · What changed
One fixed price, in writing, the same day you ask · a delivery date agreed in writing · about 4 hours of your engineers' time · the price only changes if the scope does.
NDA before anything sensitive · the drill runs on sample data · no production access · every document is yours.
In your own tools · Your team runs it · We do not become the security team
A contact point, a decision on the record, and fixes without delay when a fix is what you chose.
The CRA asks for a disclosure policy and a contact point that is not limited to automated tools. Fixes are to be provided without delay. Security updates are free, and they come with advisories. Not every vulnerability needs a patch, but the decision must be written down.
That path has to last the support period, not just the week after launch. A report that arrives in a personal inbox, with the decision living in a chat, will not survive a question about it a year later.
From the public contact to the advisory, with a hand-off when a case is actively exploited.
An intake page and a security.txt file, so a report has a front door that is not one person's email.
States and response targets that you set.
Owner and evidence for the decision, including a decision not to patch.
A fix is mapped to the release that carries it, so you can say which version has it.
A draft advisory for the update. Your team publishes it.
When a case is actively exploited, it hands off to the reporting desk and the Article 14 clocks.
An actively exploited case leaves this path and opens on the reporting desk.
If the case is actively exploited, it branches to the reporting desk.
A report gets a state, a decision, and either a release or a written reason.
A report arrives on the intake page. Triage gives it a state. Someone records the decision and the evidence. If there is a fix, it is mapped to a release and an advisory is drafted. If the case is actively exploited, it moves to the reporting desk.
We write the path into the tools you already use.
How a report reaches you today.
States, targets, and who is allowed to decide.
Intake, records, and the hand-off to reporting.
One practice report, on sample data.
Code, docs and access are yours. We stay on call for 30 days.
You get a path with a record. We need the people who will use it.
No. We set up the path and the records. Your people triage, decide and fix. You stay responsible.
We give a template for your team or adviser to adapt. We do not sign it, and it is not legal advice.
Not every vulnerability needs a patch. The decision does have to be documented, with an owner and the evidence behind it.
In practice, yes. A PSIRT is the team and process that receives, triages and answers vulnerability reports. We set up that process and its records, sized for a small product team.
Samisoftz builds the process and software your team uses to organise CRA evidence and reporting. You stay responsible for meeting the regulation. We don't give legal advice, act as a notified body, or submit reports for you.
On a delivery date agreed in writing, your team will know who decides, what to send at 24 and 72 hours, and will have practised it once on your own product. The decision to report stays with you. We set up how.
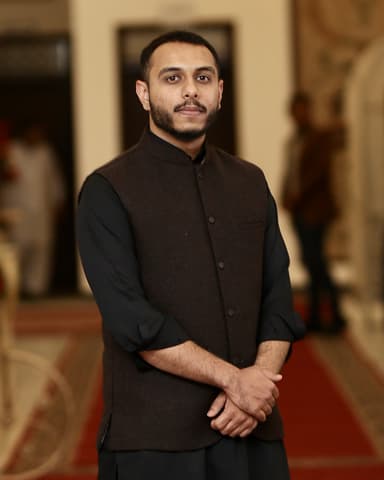
You'll talk to Usama, who'd build it.
30 minutes · no slides · a written answer if it's not a fit
One fixed price, in writing, the same day you ask · a delivery date agreed in writing · about 4 hours of your engineers' time · the price only changes if the scope does.
NDA before anything sensitive · the drill runs on sample data · no production access · every document is yours.